

Cybersecurity for healthcare providers in Dubai and the UAE
Cyber security for healthcare in the UAE has to work around clinical systems that cannot pause for maintenance and connected medical devices that cannot be taken offline to patch. iConnect provides cybersecurity for UAE hospitals and clinics: passive monitoring of the clinical estate, 24x7 detection and response, and the evidence ADHICS and the health authorities require.
Why a security decision in a hospital is also a clinical decision
In most environments, isolating a compromised machine is the first response. In a hospital that machine may be attached to a patient. The technically correct action and the clinically safe action are not always the same, and the person who understands the security event may not be the person qualified to make the clinical judgement.
The service is therefore designed differently. Detection has to be fast, but response is graduated and agreed in advance: what can be isolated immediately, what needs a clinician involved, and who holds that authority outside working hours.
The estate adds to the difficulty. Imaging systems, infusion pumps, monitors and laboratory analysers are built for a working life measured in decades, often run operating systems that no longer receive updates, and carry vendor agreements that prohibit modification. They cannot be patched or fitted with an agent.
The approach is containment: monitor what each device communicates with, segment it so that a compromise cannot spread, and keep the clinical network separate from everything that does not need to reach it.
Threats to UAE healthcare providers
Healthcare is targeted because disruption to care is serious and patient data retains its value for far longer than a card number.
What a healthcare security programme has to work around
Four conditions that determine how a security design can be operated in a live clinical environment.
The services behind a healthcare security programme
The services are built so that the clinical estate is monitored without anything being installed where it should not be.
What a UAE healthcare provider reports against
Which applies depends on the emirate you operate in and the data you hold. The controls are mapped once and evidenced from the same records.
ADHICS
The Abu Dhabi Healthcare Information and Cyber Security standard, issued by the Department of Health. Governance, asset and access management, incident handling and protection of patient information, assessed on whether controls operate.
Dubai Health Authority requirements
Providers licensed in Dubai carry information security obligations covering patient data handling, access control and incident notification, alongside the national standards.
UAE Information Assurance Standards
The national control set. Logging, access control and incident response are examined early and require documented operation over a period.
Personal Data Protection Law
Federal Decree-Law 45 of 2021. Health data is sensitive personal data, so demonstrable control over access and a record of who reached what carries particular weight.
How an engagement with a healthcare provider runs
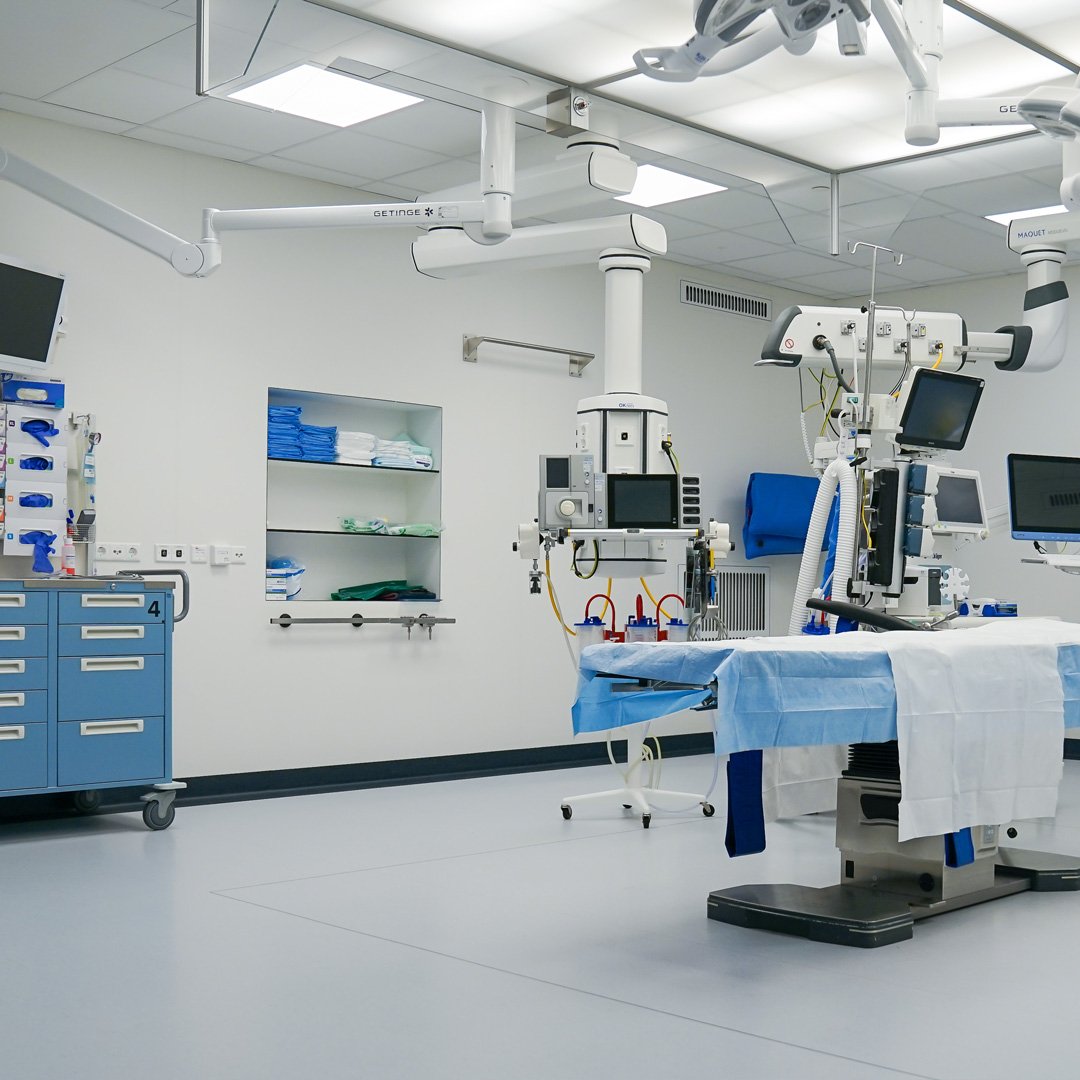
Before anything is connected, iConnect agrees with you what may be isolated automatically, what requires a clinical decision, who holds that authority out of hours, and which devices must not be touched.
- Devices under vendor restriction listed and excluded from active measures
- Clinical authority named for actions that could affect care
- Read-only, passive collection on the clinical estate
Passive discovery establishes what is on the network, including devices not on the asset list, before any detection logic is written.
- Connected medical devices discovered without touching them
- Unexpected and undocumented systems identified early
- Segmentation gaps identified from real traffic
Segmentation is tightened around what cannot be hardened, and monitoring is tuned against your own traffic so that an alert reaching a clinical environment requires attention.
- Clinical, corporate and building networks separated
- Baselines built from your traffic
- Severity levels and permitted actions agreed per level
Monthly reporting that serves both your IT team and your assessor, with rehearsal of the ransomware decision path so that the authority chain is tested before it is needed.
- Evidence assembled from daily operation
- Isolation and recovery decisions rehearsed with clinical input
- Detections added as the estate changes
Frequently asked questions about healthcare cybersecurity
The Abu Dhabi Healthcare Information and Cyber Security standard is the control set issued by the Department of Health for healthcare entities in Abu Dhabi. It covers governance, asset and access management, incident handling and the protection of patient information. Providers in Dubai answer to the Dubai Health Authority and to the UAE Information Assurance Standards, and the Personal Data Protection Law applies to patient data throughout the UAE. iConnect maps the set that applies to you once and runs the environment so that the evidence accumulates during operation.
Medical devices are secured without modifying them, because most cannot take an agent and many carry vendor conditions that void support if they are changed. Visibility is achieved passively, by monitoring what each device communicates and to whom, and devices are placed behind segmentation that limits what a compromised device can reach. The objective is to contain the device without modifying it.
No, monitoring does not interfere with clinical systems, because collection on the clinical estate is read-only and passive. Nothing is installed on a device that carries a vendor restriction, and no automated action is permitted against a clinical system without an agreed authority and a clinical safety judgement. These rules are documented before anything is connected.
The response plan is built around continuity of care. During onboarding, iConnect agrees with you which systems can be isolated immediately, which require a clinical decision, and who holds that authority outside working hours. Settling this in advance means the decision path exists before an incident occurs.
Patient data is protected by controlling and recording who can access it. Administrative access is placed under control, access to record systems is logged in a form that answers an audit question, and alerts are raised on patterns that indicate misuse as well as intrusion, such as a single account opening records with no clinical relationship to the user.
Yes, this is the usual arrangement. iConnect supplies the monitoring, the analysts and the detection engineering, and your IT team keeps ownership of the environment. Escalation paths and responsibilities are agreed at the start of the engagement.